ZTE Wantong ISG F-Series · Xinchuang Firewalls
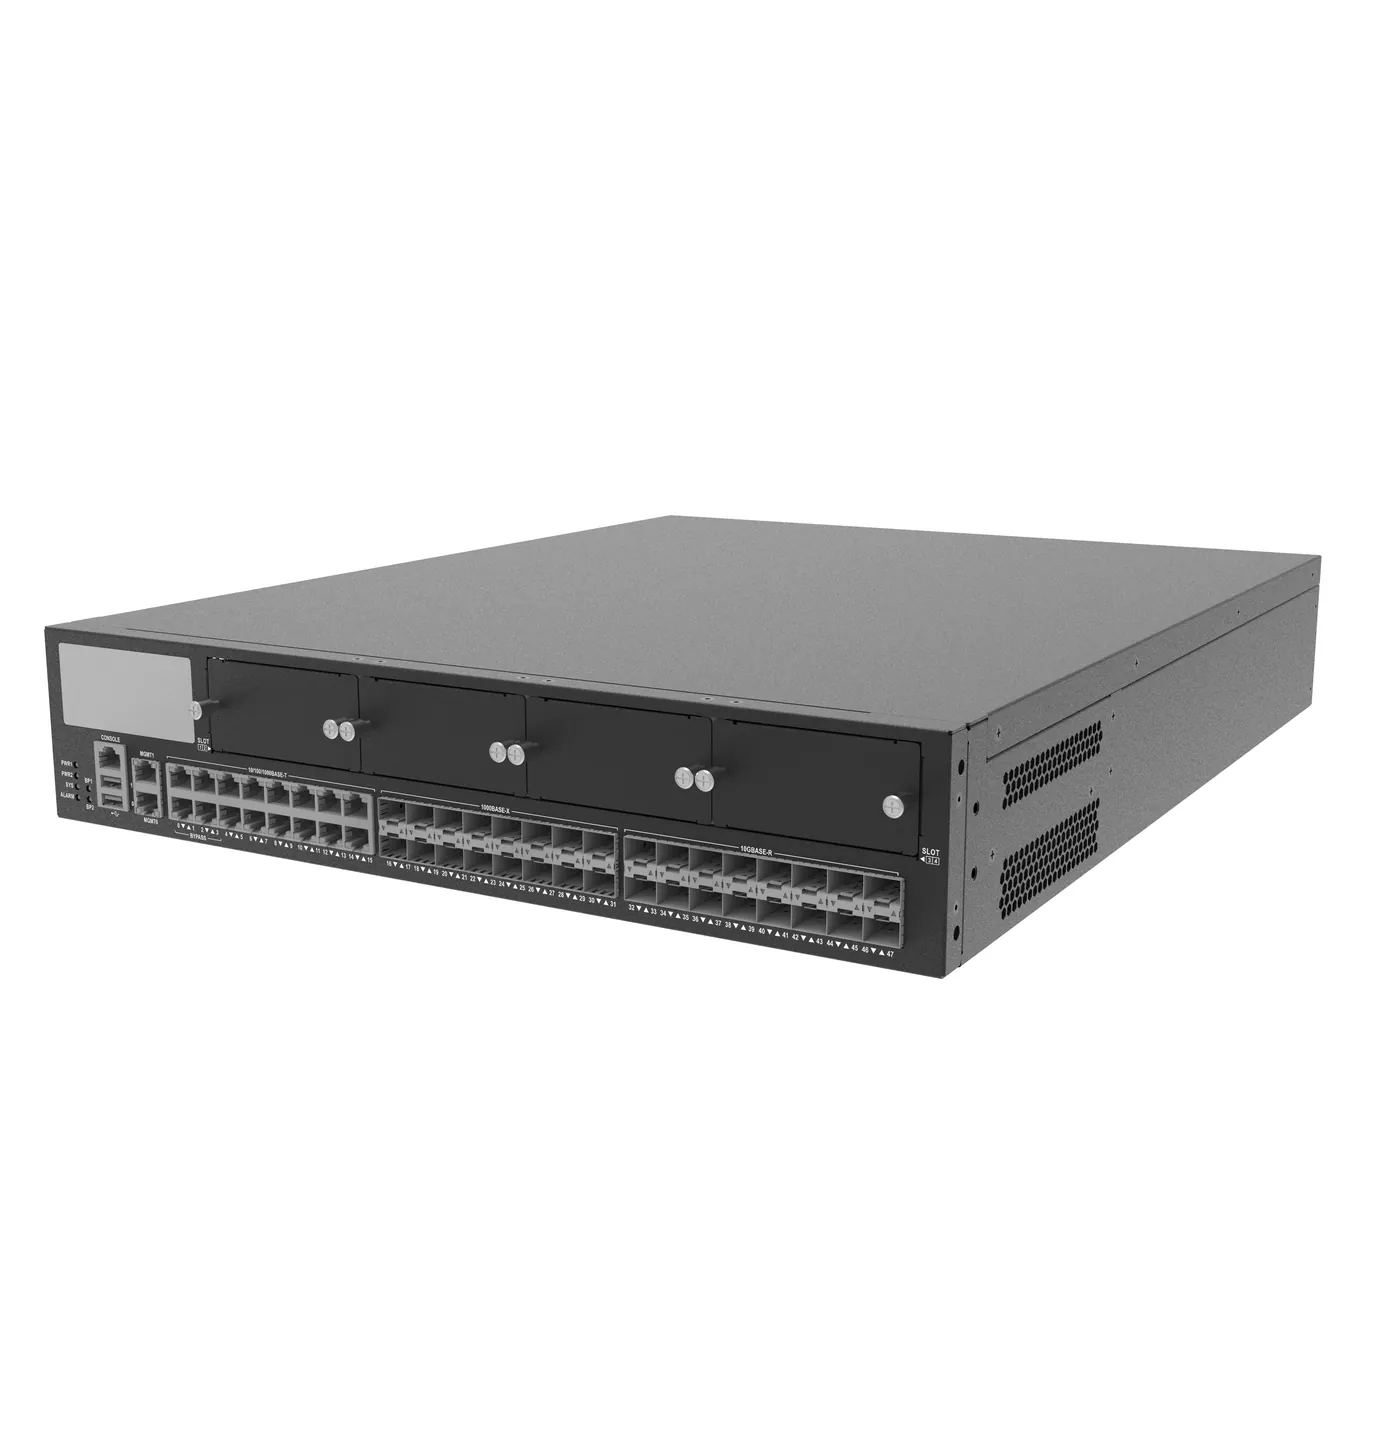
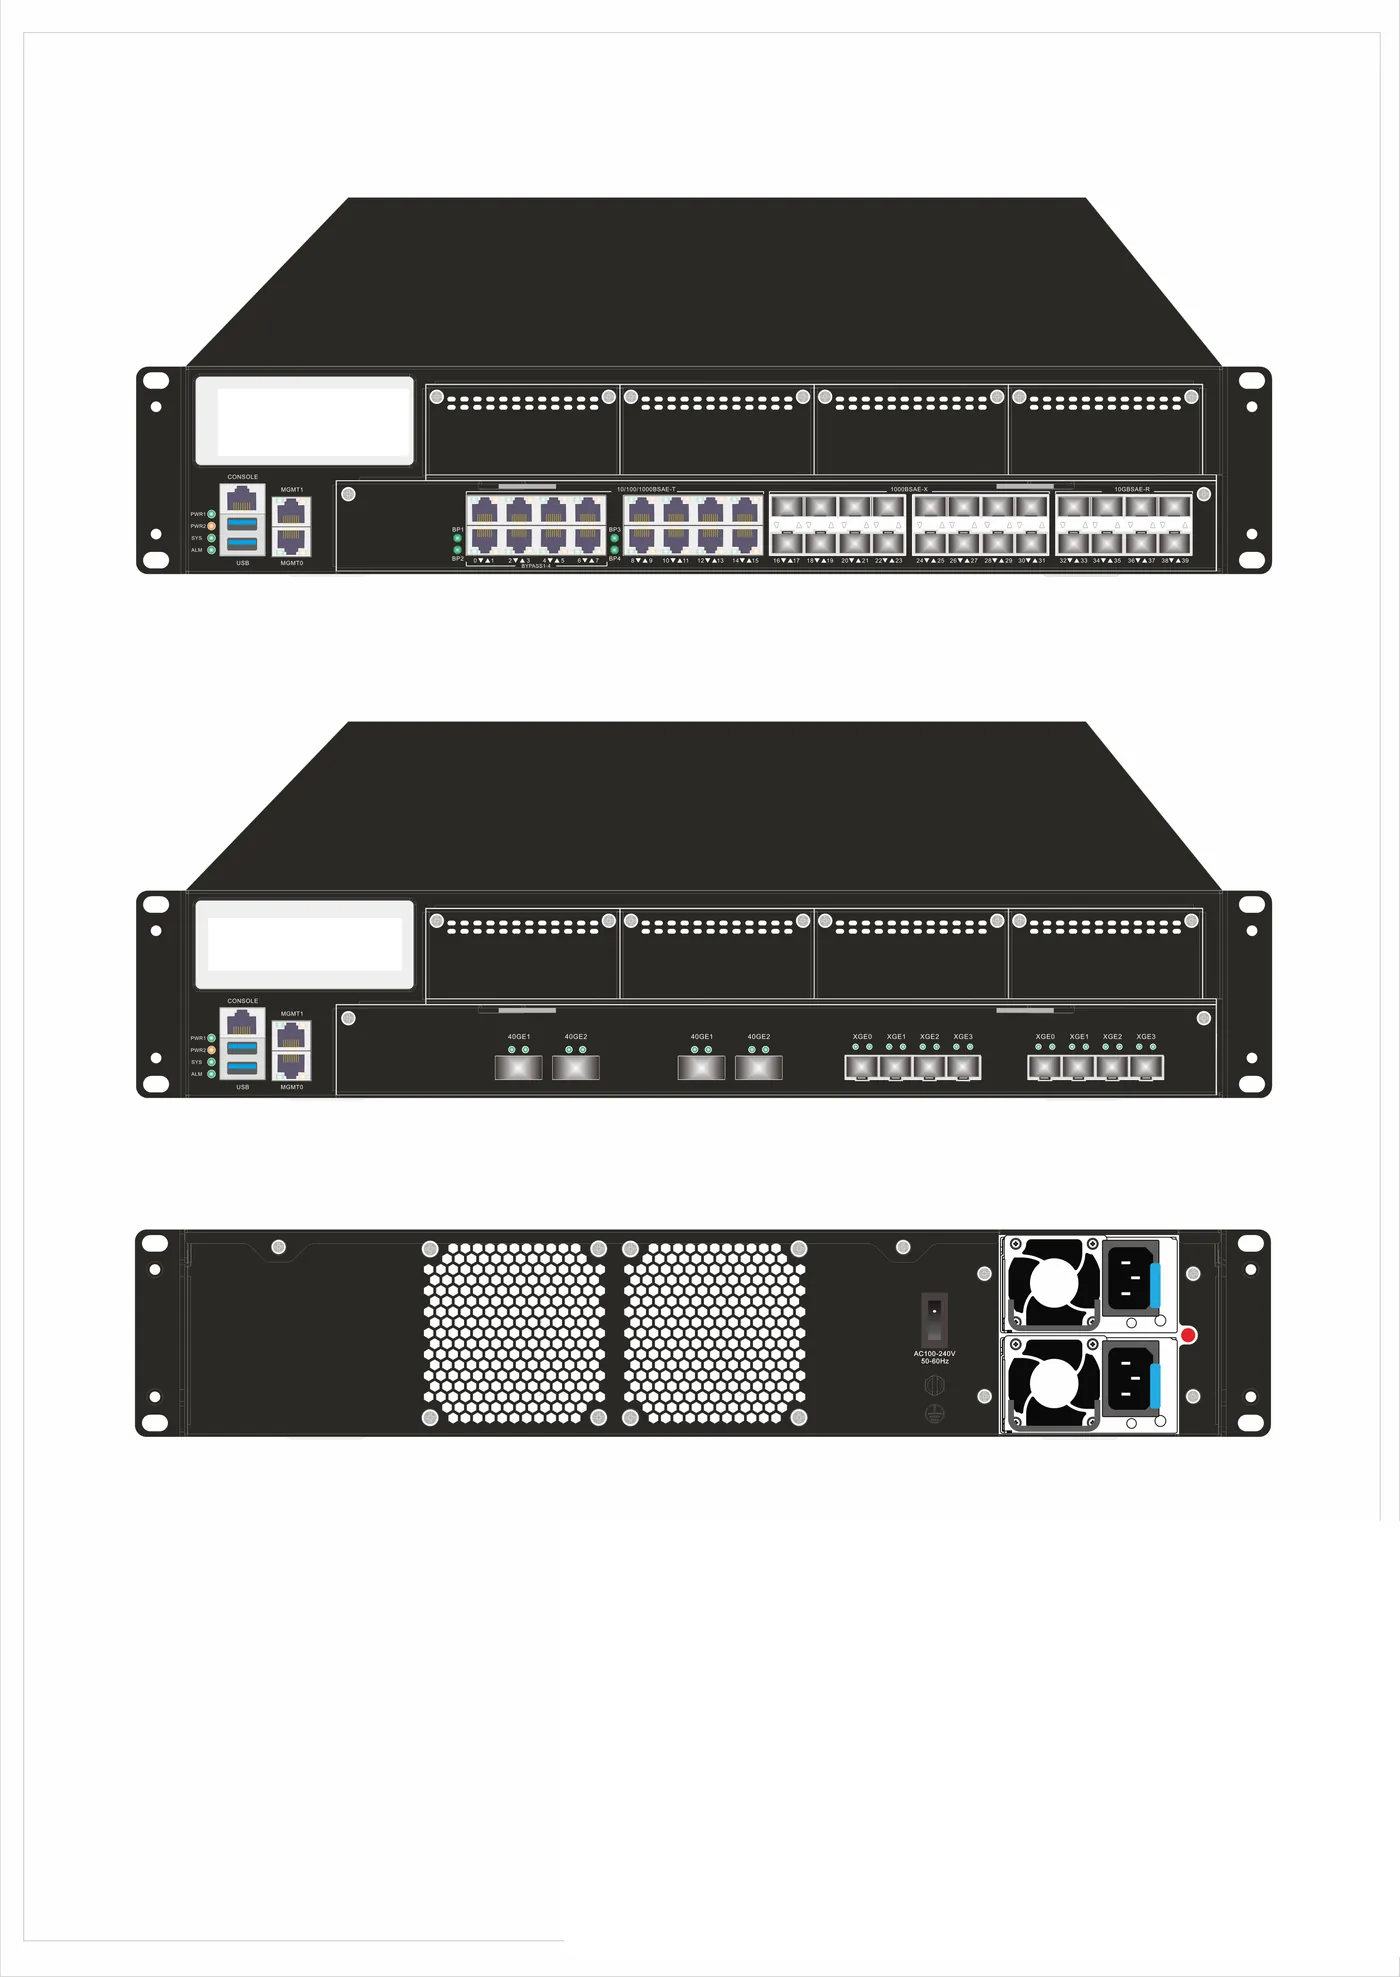
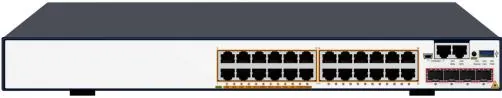
Ten firewalls from a 2 Gbps desktop unit for a branch office to a 240 Gbps modular chassis for a data center edge, all running the same software: unified security policy, intrusion prevention, antivirus, web protection, IPSec VPN, user authentication and attack-chain analysis. We deliver them configured as part of the network solutions we build.
Lead time · In stock: at your forwarder’s China warehouse 3 days after payment · Not in stock: 7–15 working days · Then air 5–10 days / sea 25–45 days to your port
Terms · Sample orders welcome · Quotation / PI fixes models, prices, Incoterms (EXW or FOB, each quoted separately), lead time and T/T payment · Defective units: free spare units agreed per order (quantity depends on order size) and written into the quotation · Warranty: up to 5 years on Zhongxin Shutong industrial switches, manufacturer warranty on other brands · Full terms, warranty & RMA
Need the PDF datasheet? Get it on WhatsApp →Sample quantities are welcome — testing one or two units first is the normal way to start.
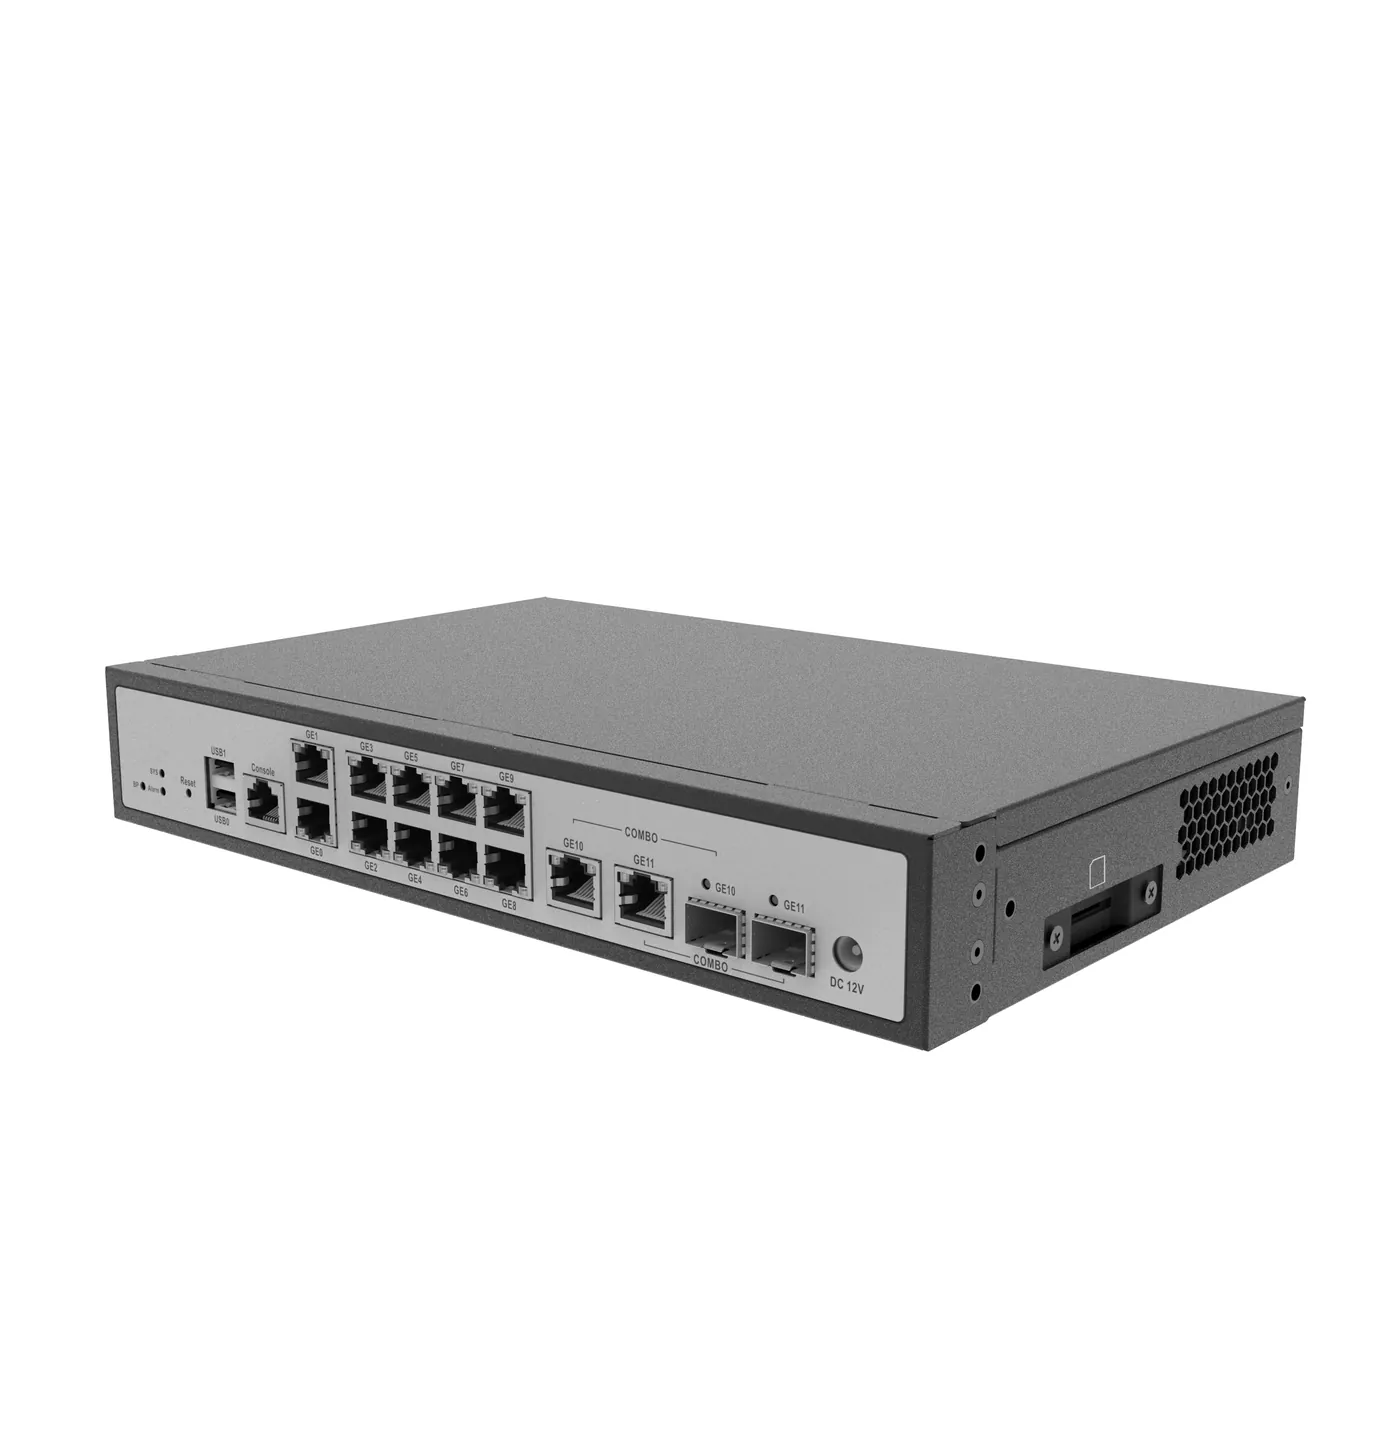
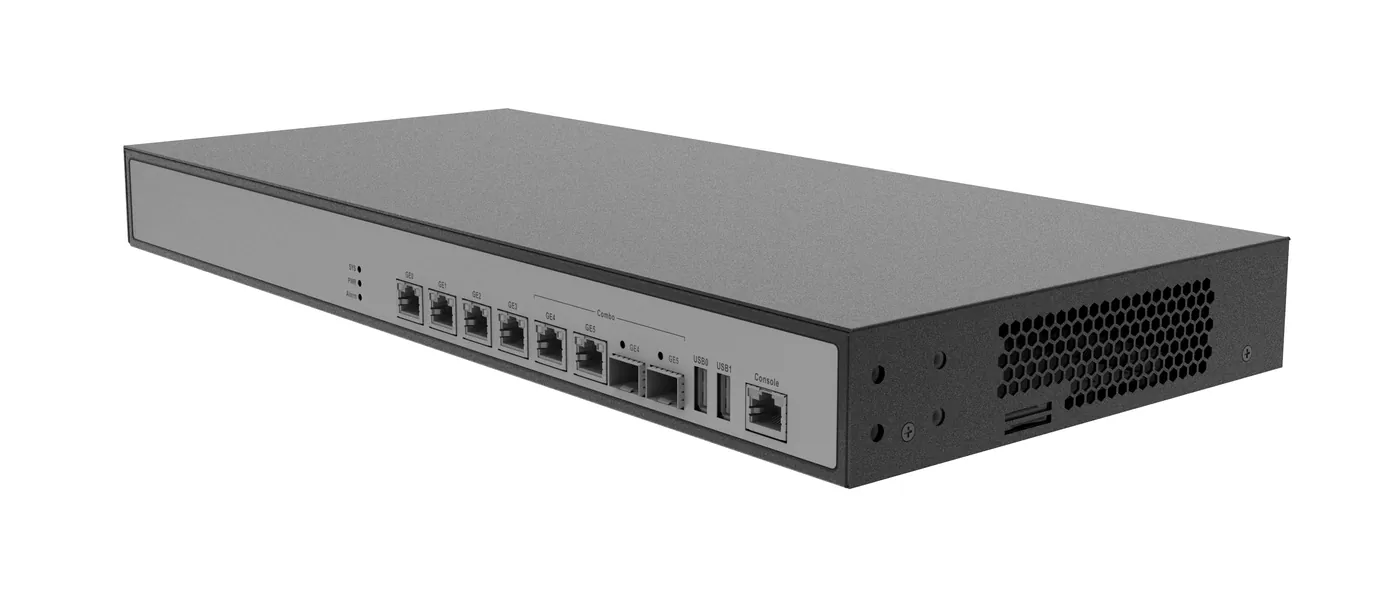
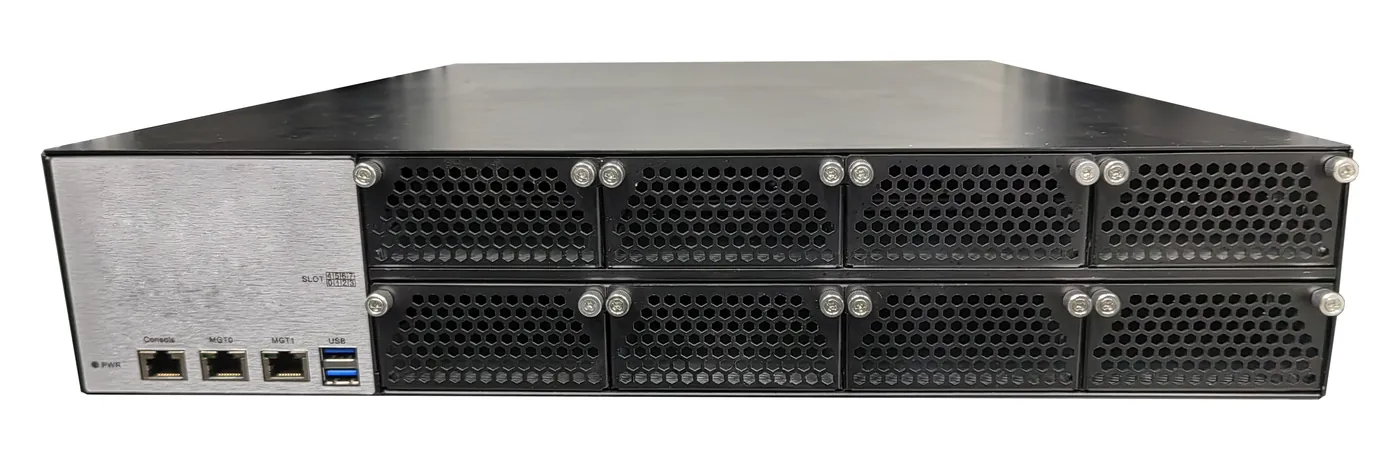
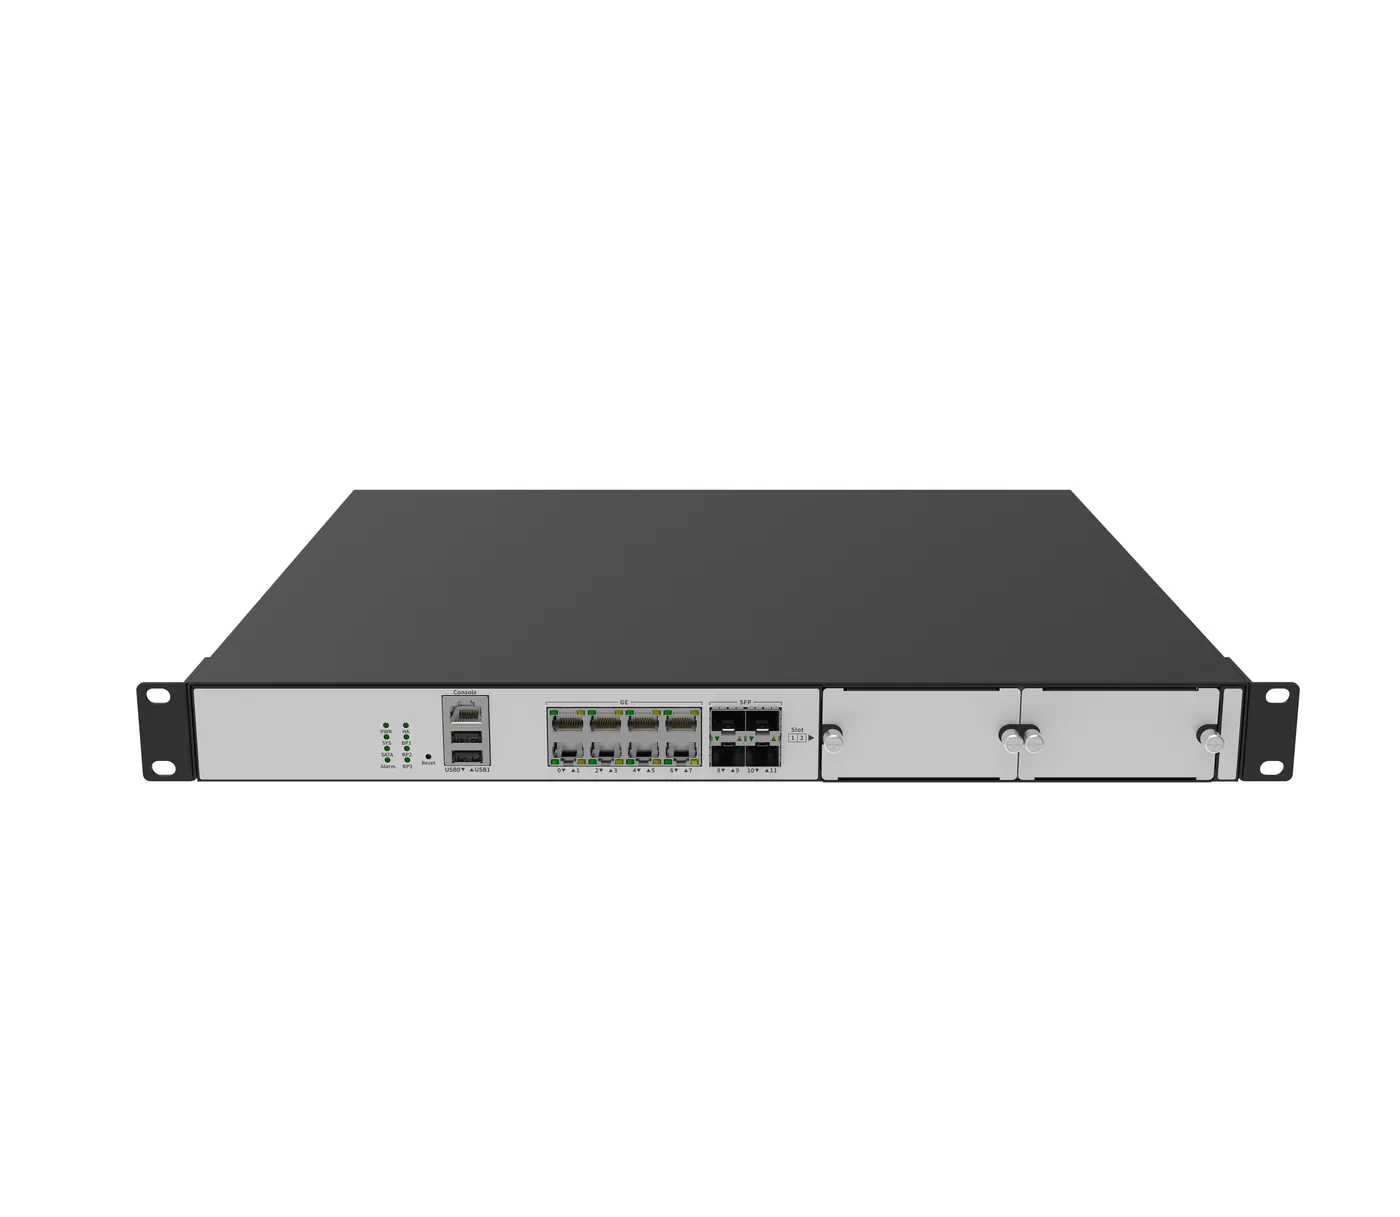
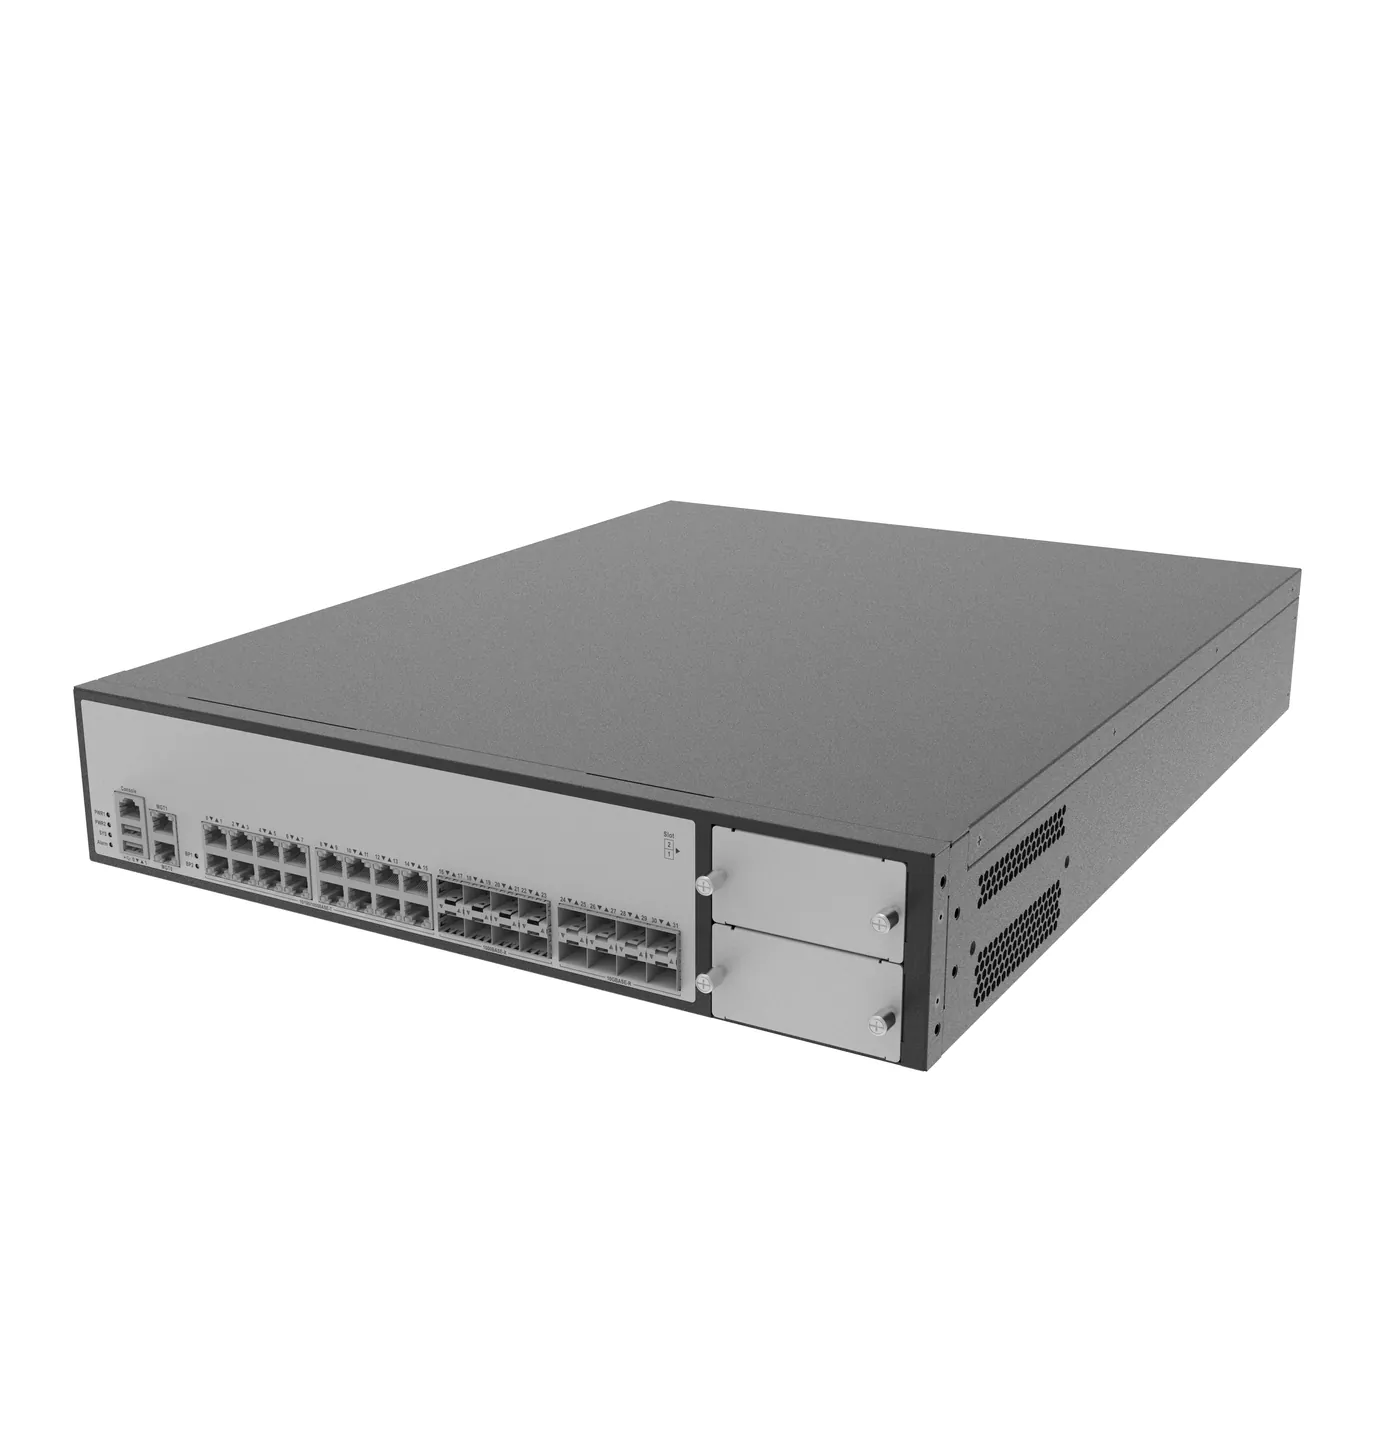
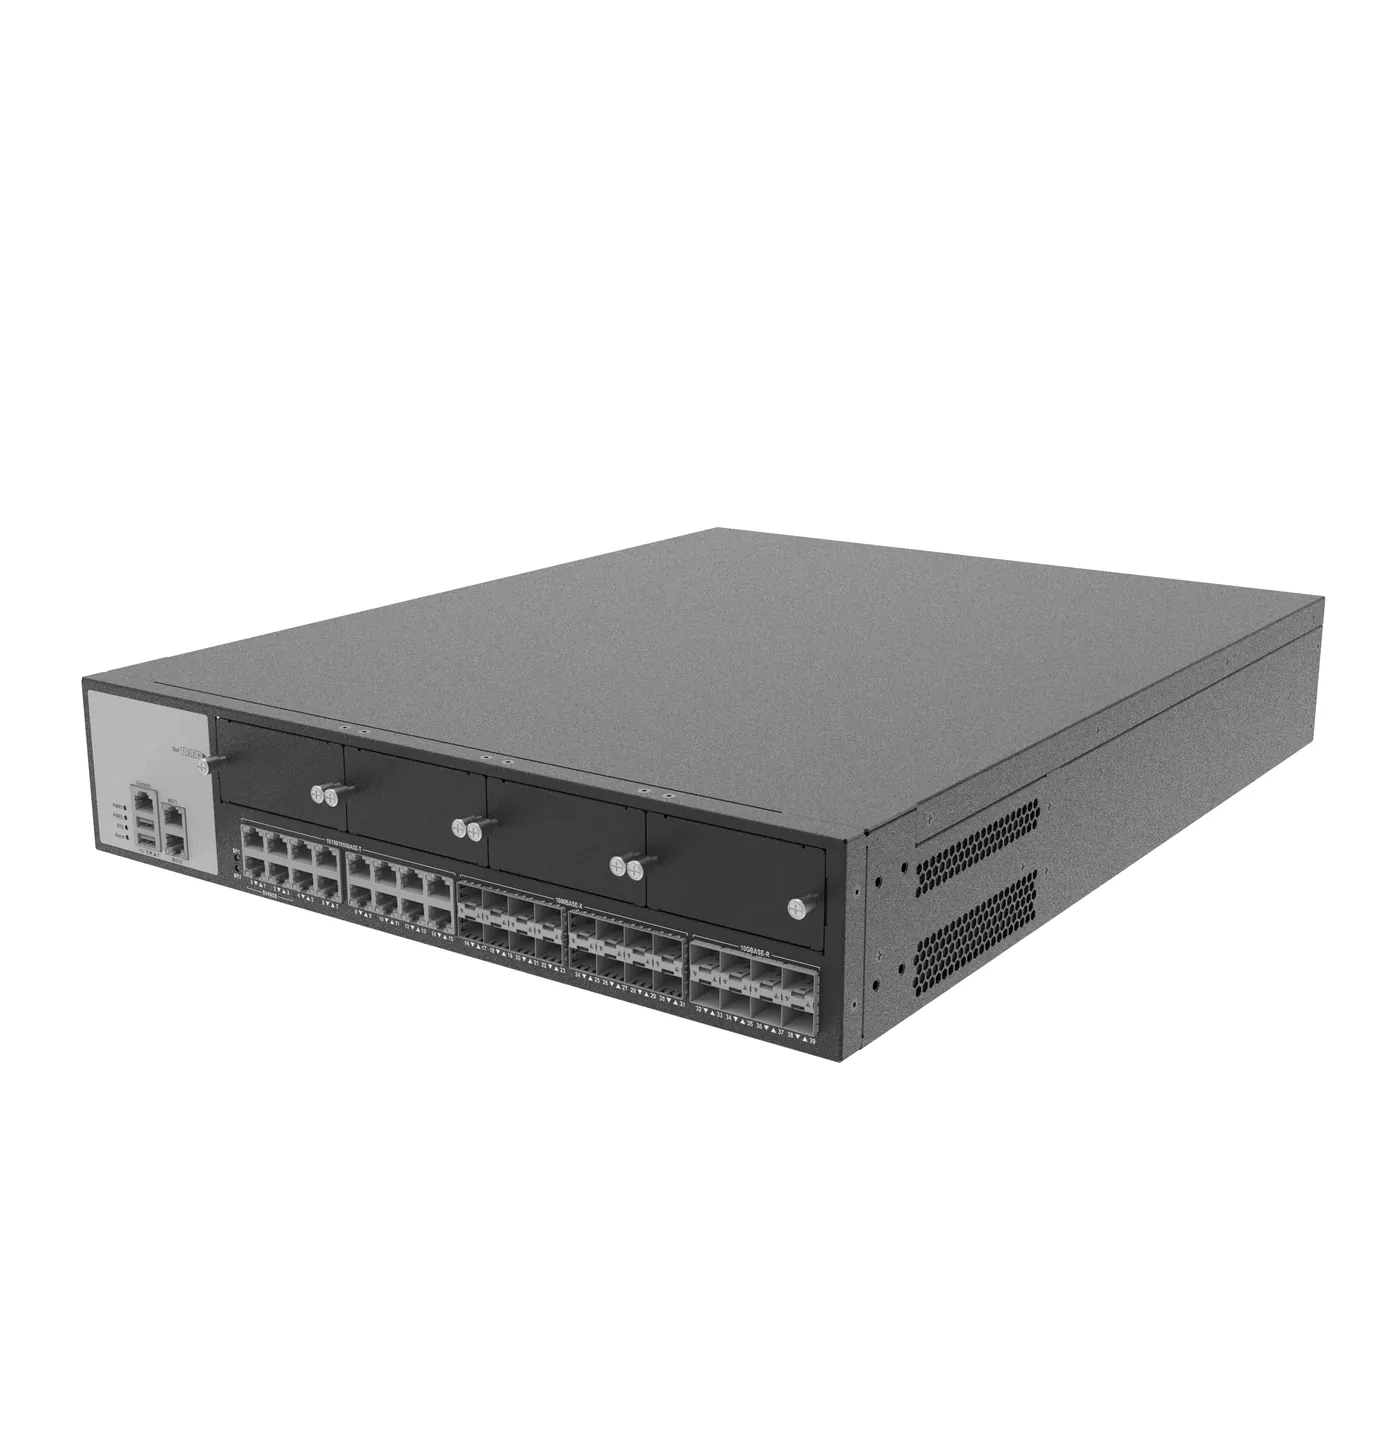
The ZTE Wantong ISG F-series is a family of Xinchuang firewalls — "Xinchuang" (信创) refers to China's domestic IT-innovation hardware and software platform, and each model lists its processor: Rockchip RK3566, Phytium E2000Q, D2000/8 or D3000, or Hygon 7280 or 3490. All ten models run the same security software: one policy matches interface, address, user, application, service, time, terminal type, VLAN ID and DSCP, and applies application control, URL filtering, intrusion prevention and antivirus together. Routing, transparent, off-path and hybrid deployment, static/RIP/OSPF/BGP routing, NAT and IPSec VPN are built in, with active-active or active-standby HA. Firewall throughput runs from 2 Gbps (F0210X) to 240 Gbps (F24028X). Specifications below are quoted from the manufacturer's datasheets — fields they do not publish are left out.
Three performance classes, one security software
How the ten models split by throughput, sessions and hardware — so you size the firewall to the site, not the other way round.
Is this the right firewall series for you?
Three typical sites and the class that fits each.
- Internet behaviour management and user authentication without a full firewall — that's the ZTE Wantong ISG A-series gateways (A1300 / A1600)
- A plain branch router for WAN access and VPN — that's the ZTE Wantong ISG access routers (ISG 1800-2S / 2800-4 / 3800-8)
- Aggregation or core routing for a carrier or large multi-site network — that's the ZTE Wantong ISG 5800 / 6800 routers
Worried about the source? Order under your own company name.
For corporate buyers: we support submitting the purchase order to the manufacturer under your company's real name — your company appears on the official order, so the origin of the goods can be verified directly with the factory. Just provide your company name and pay by corporate bank transfer.
Using your own freight forwarder? No problem.
For small and mid-size orders, we deliver directly to your designated forwarder's warehouse in China — EXW or FOB, your choice, each quoted separately. From hand-over onward, international shipping and destination-side arrangements are handled by your forwarder — the way you already work.
Key Features
The series capability list — from the manufacturer's datasheet.
Who uses it, where it goes and how to size the firewall
Written for the ZTE Wantong ISG F-series from its own specifications: 10 models from 2 to 240 Gbps firewall throughput, 1.3 to 150 million concurrent sessions, IPS, antivirus, web protection, IPSec VPN and active-active or active-standby HA.
Who it is for
- Integrators securing SME and branch networks — An F0210X or F0510X at each site gives NAT, IPS, antivirus, URL filtering and an IPSec tunnel to head office in one box, and with central management new branch VPNs come online without configuring each tunnel by hand.
- Schools, hospitals and public Wi-Fi operators — Many users who must be identified: Portal, SMS, QR code, RADIUS, LDAP or AD single sign-on authentication, per-user audit logs kept beyond 180 days, and reports by user and application.
- Companies publishing web services — Web protection with CSRF and CC attack defence, anti-tampering and anti-hotlinking sits in front of the web servers, with destination NAT and server load balancing on the same unit.
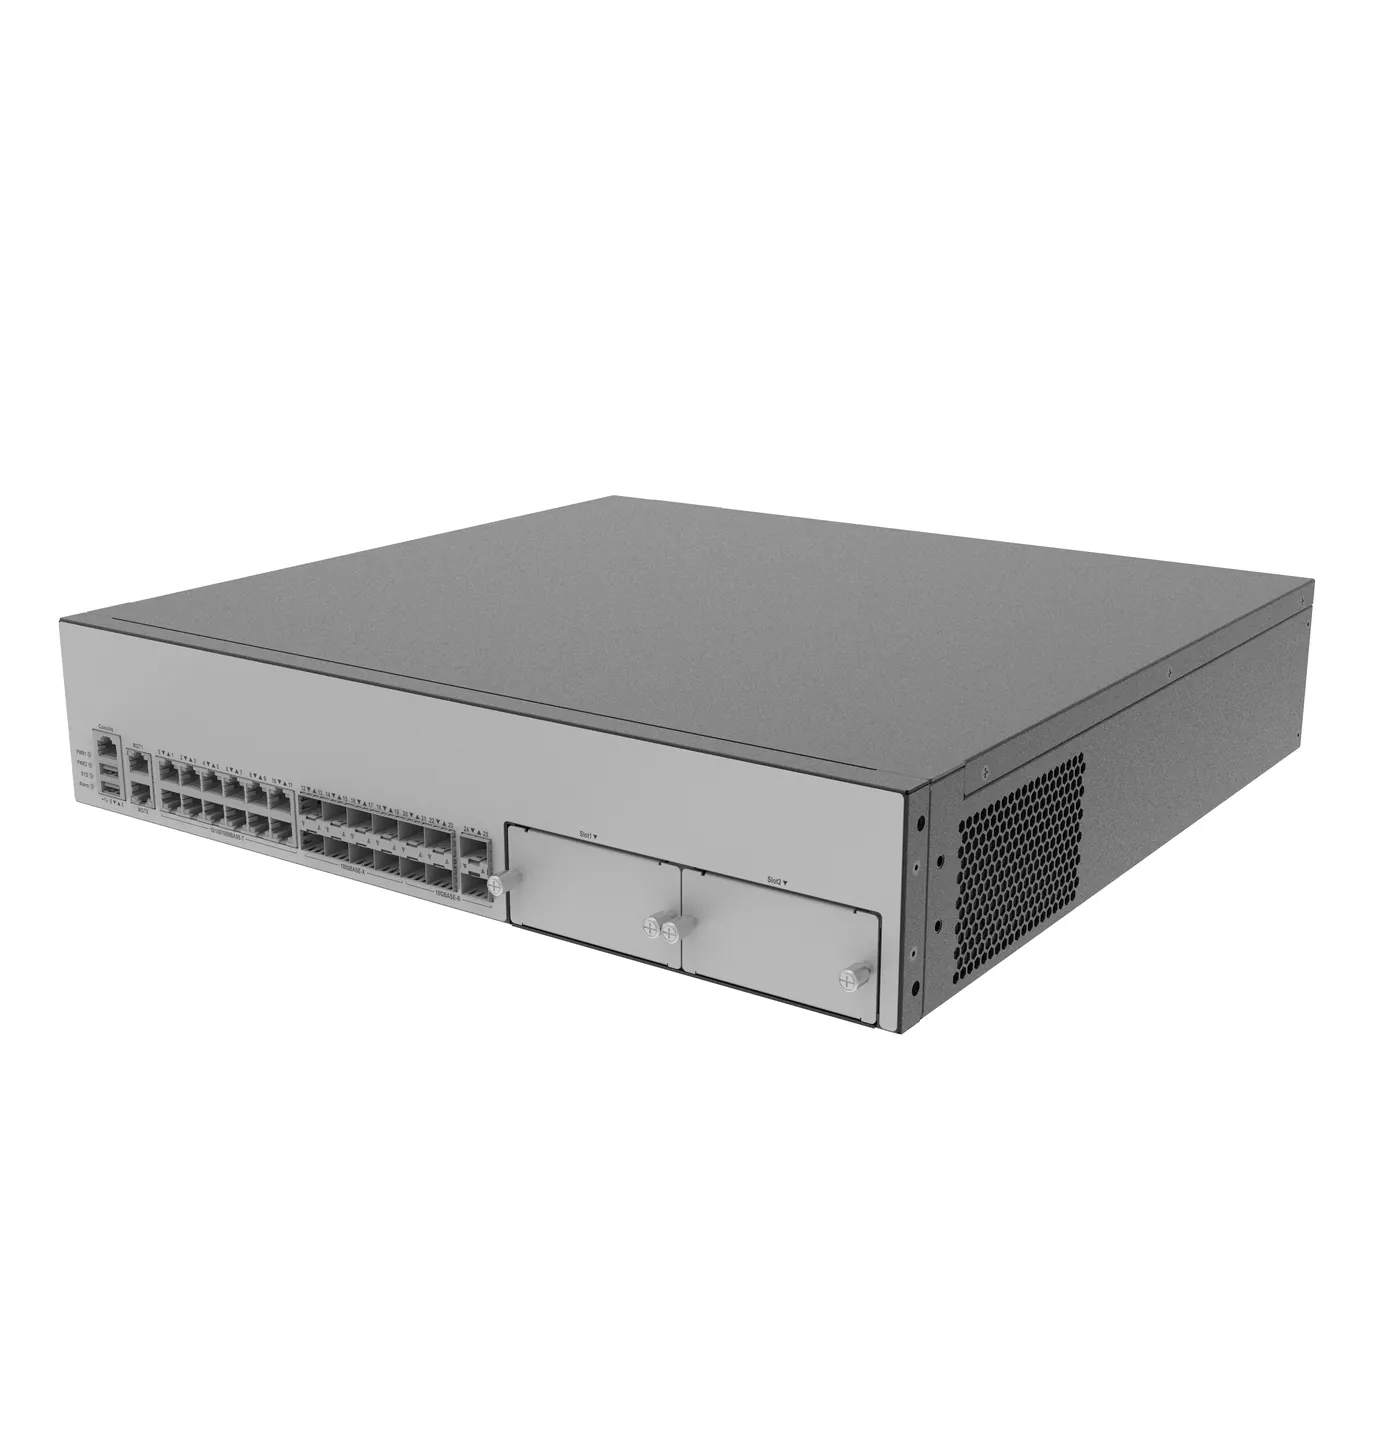
- Data center and large campus operators — An HA pair of F8024X or F24028X units handles 80–240 Gbps and 80–150 million sessions at the perimeter, with two dedicated out-of-band management ports and dual 550 W power supplies per unit.
Where it goes
- Internet edge — Routing mode between the ISP lines and the core switch: NAT, ISP routing and link load balancing across several lines, with the security policy applied to all outbound and inbound traffic.
- Inline without readdressing — Transparent bridge mode drops into an existing link with no IP address on the firewall; antivirus still scans in this mode, and hardware bypass keeps the link up if the unit fails.
- Off-path monitoring — Off-path (bypass) deployment on a mirrored switch port for audit and threat visibility without touching the live traffic path.
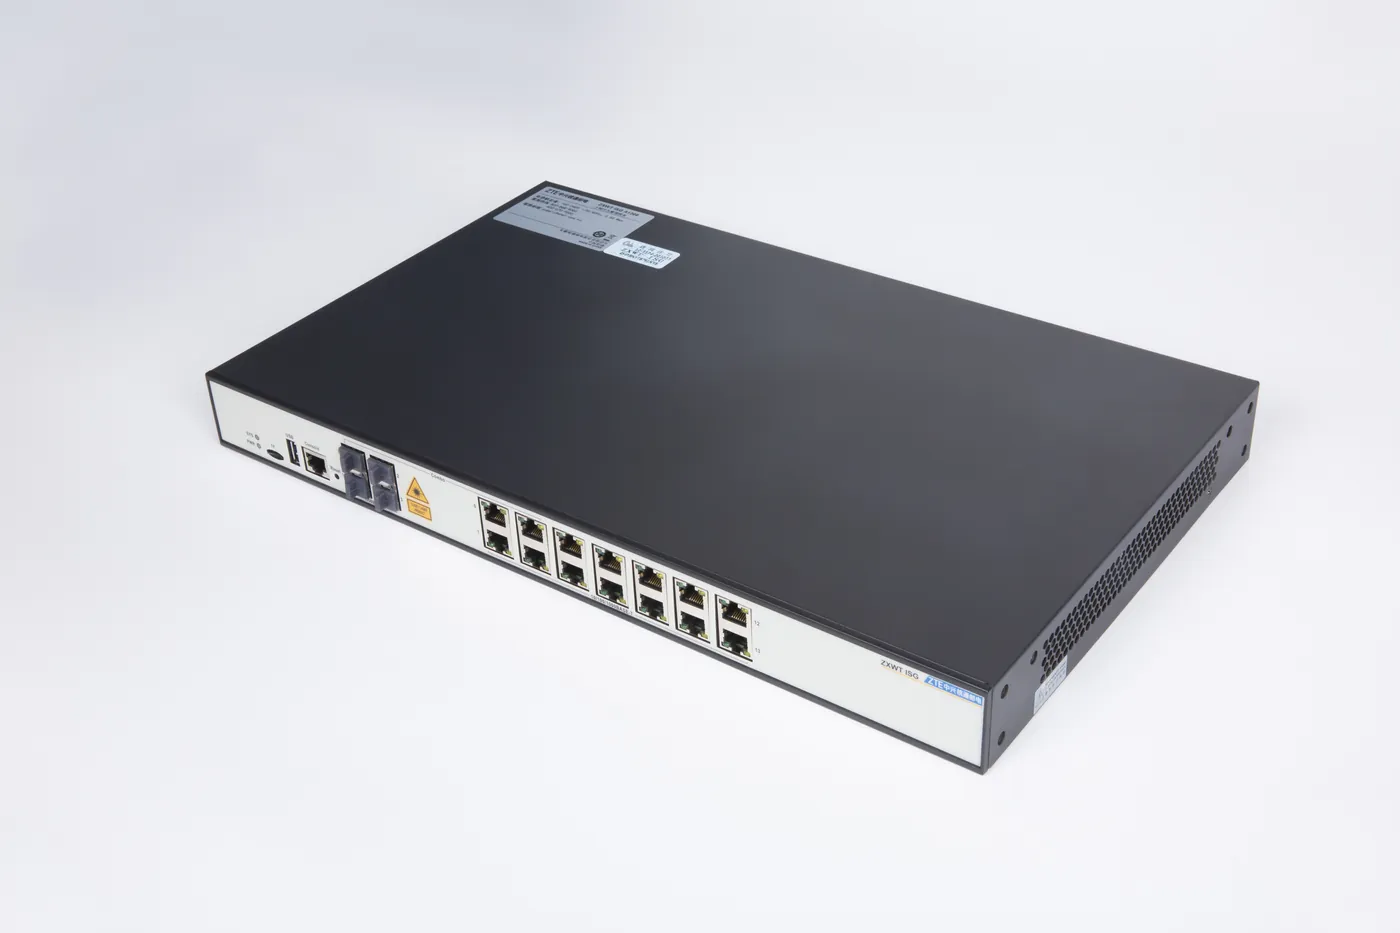
- Branch offices — The 275 mm-wide F0210X fits a small cabinet or a desk; it terminates the local internet line and builds the IPSec tunnel to the head-office firewall.
- Equipment room rack — The other nine models are 19-inch rack units, 1U (44 mm) or 2U (88–89 mm) high and 200 to 600 mm deep; the F24028X needs 600 mm of depth plus cabling space.
ISG F-series sizing: which of the 10 models
All ten run the same firewall, IPS, antivirus and VPN software; they differ in throughput, session capacity, interfaces, slots and power redundancy. Compare your total internet bandwidth with the application-layer throughput, and your peak connection count with concurrent sessions and new sessions per second. The datasheets give no user counts, so the typical site size row is our guidance, not a manufacturer figure.
| F0210X | F0510X | F1212X | F1522X | F24028X | F3312X | F3322X | F4024X | F6024X | F8024X | |
|---|---|---|---|---|---|---|---|---|---|---|
| Firewall throughput | 2 Gbps | 5 Gbps | 12 Gbps | 15 Gbps | 240 Gbps | 33 Gbps | 33 Gbps | 40 Gbps | 60 Gbps | 80 Gbps |
| Application-layer throughput | 2 Gbps | 3 Gbps | 7.5 Gbps | 7.5 Gbps | 126 Gbps | 22 Gbps | 25.3 Gbps | 22.7 Gbps | 22.85 Gbps | 80 Gbps |
| Concurrent sessions | 1.3 M | 2 M | 8 M | 25 M | 150 M | 20 M | 25 M | 50 M | 50 M | 80 M |
| New sessions per second | 75,000 | 80,000 | 100,000 | 100,000 | 2,000,000 | 290,000 | 270,000 | 270,000 | 300,000 | 1,420,000 |
| Fixed interfaces | 10×GE + 2×Combo | 4×GE + 2×Combo | 10×GE + 4×Combo | 12×GE + 8×SFP + 6×SFP+ | none | 8×GE + 4×SFP | 16×GE + 8×SFP + 8×SFP+ | 16×GE + 16×SFP + 8×SFP+ | 16×GE + 16×SFP + 16×SFP+ | 16×GE + 16×SFP + 8×SFP+ |
| Expansion slots | — | — | 2 | — | 8 | 2 | 2 | 4 | 4 | 4 |
| Bypass pairs | 1 | 1 | 3 | 3 | — | 3 | 2 | 2 | 2 | 2 |
| Power supply | single, 24 W | single, 25 W | dual, 60 W × 2 | dual, 150 W × 2 | dual, 550 W × 2 | dual, 150 W × 2 | dual, 150 W × 2 | dual, 550 W × 2 | dual, 550 W × 2 | dual, 550 W × 2 |
| Height (from dimensions) | 44 mm, 275 mm wide | 1U | 1U | 2U | 2U | 1U | 2U | 2U | 2U | 2U |
| Typical site size (our guidance) | small office / branch | branch / small site | SME head office | mid-size site, 10G uplinks | data center / large campus edge | mid-size campus | head office / campus, 10G | large campus / multi-site HQ | large campus, dense 10G | large campus / data center edge |
- Size on the application-layer figure: a 10 Gbps internet feed with IPS and application control turned on is above the F1212X and F1522X (7.5 Gbps each) and within the F3312X (22 Gbps) or F3322X (25.3 Gbps).
- The F8024X and F24028X stand out on new sessions per second (1.42 million and 2 million, against 270,000–300,000 on the F4024X and F6024X) — choose them where many short connections arrive at once, such as large public Wi-Fi or busy published services.
- For HA, order two identical units; on mid-range and high-end models, also feed the two power supplies of each unit from separate circuits.
— = not listed in the datasheet / not applicable. Values are from the specification tables; 1U/2U is read from the listed heights (44 mm and 88–89 mm). Session counts are rounded to millions (M) from the datasheet figures. The typical site size row is our guidance, not a manufacturer figure.
Full Specifications — Model by Model
Series specifications with one column per model — technical values in English. The highlighted column follows your model selection above.
ISG F-Series — Entry Models: Hardware & Performance (2 models)
| Item | F0210X | F0510X |
|---|---|---|
| Processor | Rockchip RK3566 | Phytium E2000Q |
| Fixed service interfaces | 10× GE RJ45 + 2× Combo | 4× GE RJ45 + 2× Combo |
| Management interface | Any service port | |
| Console | 1× RS232 (RJ45) | |
| Bypass | 1 pair | |
| Power supply | Single power supply | |
| Firewall throughput (UDP 1518 bytes) | 2 Gbps | 5 Gbps |
| Application-layer throughput | 2 Gbps | 3 Gbps |
| Concurrent sessions | 1,300,000 | 2,000,000 |
| New connections per second | 75,000 | 80,000 |
| HA | Active-active / active-standby | |
| Weight (default configuration) | 1.47 kg | 4.5 kg |
| Dimensions (L × H × D) | 275 × 44 × 175 mm | 440 × 44 × 200 mm |
| Rated input voltage | 100–240 V AC | |
| Maximum power | 24 W | 25 W |
| Temperature | Operating 0°C to 40°C; storage -40°C to 70°C | |
| Humidity | 5%–90% operating, non-condensing | |
ISG F-Series — Mid-Range Models: Hardware & Performance (4 models)
| Item | F1212X | F1522X | F3312X | F3322X |
|---|---|---|---|---|
| Processor | Phytium E2000Q | Phytium E2000Q | Phytium D2000/8 | Phytium D2000/8 |
| Fixed service interfaces | 10× GE RJ45 + 4× Combo | 12× GE RJ45 + 8× GE SFP + 6× 10GE SFP+ | 8× GE RJ45 + 4× GE SFP | 16× GE RJ45 + 8× GE SFP + 8× 10GE SFP+ |
| Expansion slots | 2 module slots | Not listed | 2 module slots | 2 module slots |
| Management interface | Any service port | Any service port | Any service port | 2× dedicated out-of-band GE management ports |
| Console | 1× RS232 (RJ45) | |||
| Bypass | 3 pairs | 3 pairs | 3 pairs | 2 pairs |
| Power supply | Dual power supplies | |||
| Firewall throughput (UDP 1518 bytes) | 12 Gbps | 15 Gbps | 33 Gbps | 33 Gbps |
| Application-layer throughput | 7.5 Gbps | 7.5 Gbps | 22 Gbps | 25.3 Gbps |
| Concurrent sessions | 8,000,000 | 25,000,000 | 20,000,000 | 25,000,000 |
| New connections per second | 100,000 | 100,000 | 290,000 | 270,000 |
| HA | Active-active / active-standby | |||
| Weight (default configuration) | 4.8 kg | 7.58 kg | 5.2 kg | 10.05 kg |
| Dimensions (L × H × D) | 440 × 44 × 400 mm | 440 × 88 × 415 mm | 440 × 44 × 400 mm | 440 × 88 × 550 mm |
| Rated input voltage | 100–240 V AC | |||
| Maximum power | 60 W × 2 | 150 W × 2 | 150 W × 2 | 150 W × 2 |
| Temperature | Operating 0°C to 40°C; storage -40°C to 70°C | |||
| Humidity | 5%–90% operating, non-condensing | |||
ISG F-Series — High-End Models: Hardware & Performance (4 models)
| Item | F24028X | F4024X | F6024X | F8024X |
|---|---|---|---|---|
| Processor | Hygon 7280 | Phytium D2000/8 | Phytium D3000 | Hygon 3490 |
| Fixed service interfaces | None (interfaces by expansion modules) | 16× GE RJ45 + 16× GE SFP + 8× 10GE SFP+ | 16× GE RJ45 + 16× GE SFP + 16× 10GE SFP+ | 16× copper + 16× GE fibre + 8× 10GE fibre |
| Expansion slots | 8 module slots | 4 module slots | 4 module slots | 4 module slots |
| Management interface | 2× dedicated out-of-band GE management ports | |||
| Console | 1× RS232 (RJ45) | |||
| Bypass | None | 2 pairs | 2 pairs | 2 pairs |
| Power supply | Dual power supplies | |||
| Firewall throughput (UDP 1518 bytes) | 240 Gbps | 40 Gbps | 60 Gbps | 80 Gbps |
| Application-layer throughput | 126 Gbps | 22.7 Gbps | 22.85 Gbps | 80 Gbps |
| Concurrent sessions | 150,000,000 | 50,000,000 | 50,000,000 | 80,000,000 |
| New connections per second | 2,000,000 | 270,000 | 300,000 | 1,420,000 |
| HA | Active-active / active-standby | |||
| Weight (default configuration) | 17 kg | 12.09 kg | 12.68 kg | 12 kg |
| Dimensions (L × H × D) | 440 × 88 × 600 mm | 435 × 89 × 550 mm | 435 × 89 × 550 mm | 440 × 89 × 560 mm |
| Rated input voltage | 100–240 V AC | |||
| Maximum power | 550 W × 2 | |||
| Temperature | Operating 0°C to 40°C; storage -40°C to 70°C | |||
| Humidity | 5%–90% operating, non-condensing | |||
ISG F-Series — Software Features (all models)
| Item | F0210X | F0510X | F1212X | F1522X | F24028X | F3312X | F3322X | F4024X | F6024X | F8024X |
|---|---|---|---|---|---|---|---|---|---|---|
| Deployment modes | Transparent bridge / routing / off-path (bypass) / hybrid | |||||||||
| Interfaces | VLAN sub-interfaces / bridge interfaces / aggregated interfaces / 802.1Q | |||||||||
| Routing | IPv4/IPv6 dual stack / static / RIP / OSPF / BGP / policy routing / application routing / ISP routing / VRF / GRE / DDNS | |||||||||
| Load balancing | Link load balancing / server load balancing / multiple egress links | |||||||||
| NAT | Source and destination NAT / one-to-one, one-to-many, many-to-many / NAT44 | |||||||||
| DHCP | DHCP relay / DHCP server / DHCP client | |||||||||
| Security policy | Unified policy matching source/destination interface and address, user, application, service, time, terminal type and model, VLAN ID, DSCP / application filtering, URL filtering, IPS and antivirus in one rule / analysis of conflicting, redundant, hidden, mergeable, empty, expired, ignored and risky-port policies | |||||||||
| Application audit and control | Online communities, P2P, file transfer, e-commerce, IM, stock trading, streaming media, online games, remote control, HTTPS websites, mail and search / audit by user, IP, application, action, content, terminal OS and device type / website, mail, forum post and search keyword filtering / built-in URL categories, malicious URL and custom URL filtering | |||||||||
| Session control | Address-object limits / per-source-IP session and new-session-rate limits / per-IP connection statistics (state, protocol, application, duration) | |||||||||
| Intrusion prevention | 8,600+ signatures, weekly rule updates / BPS level 5 detection rate > 95% (manufacturer figure) / 4 predefined templates (privilege escalation, arbitrary code execution, trojan/backdoor, web attack) / custom rules / protocol-evasion detection / attack source tracing / HTTP control over 7 fields and 10 conditions with regular expressions | |||||||||
| Antivirus | 4 million+ virus signatures / HTTP, SMTP, FTP, POP3, IMAP / up to 20 layers of ZIP/RAR archives / MD5 file and domain whitelists / scanning in routing, transparent (no IP), hybrid and VPN modes / policies by source/destination IP, service, time, interface, user | |||||||||
| Web protection | Predefined web-attack signatures / precise HTTP access control / anti-hotlinking / CSRF and CC attack protection / web page anti-tampering / application hiding / crawler identification and filtering / content keyword filtering / HTTP protocol and URL parameter compliance checks | |||||||||
| Other protection | Abnormal-packet attack defence / DoS protection / brute-force protection / weak-password protection / illegal outbound connection protection / compromised host detection / behaviour model | |||||||||
| Risk scanning | Port scanning / weak-password scanning | |||||||||
| Security analysis | Attack-chain analysis by asset and by attacker (early, intrusion, control, exfiltration stages) with drill-down / asset discovery by active scanning and traffic monitoring (PC, switch, printer...) and asset risk rating / web protection statistics and top 10 attacked URLs | |||||||||
| Logs and reports | Traffic trends, distribution and top-N by user and application / device health (CPU, memory, throughput, sessions) / user behaviour tracking / audit logs for IM, communities, search, mail, file transfer, websites, attacks, malicious URLs and system operations / HTTPS and mail decryption and audit / log retention beyond 180 days / Syslog with level filtering | |||||||||
| User management | Tree-structured user groups, bulk import/export / local, RADIUS, LDAP and static IP-bound users, custom attributes / online user view with log-off, freeze and unfreeze | |||||||||
| Authentication | Local, Portal, RADIUS, LDAP, POP3, AD single sign-on, SMS, WeChat official account, app, IC card, QR code, DingTalk, hybrid and no authentication / user self-registration with administrator approval / integration with third-party authentication servers / user identification from RADIUS and HTTP traffic | |||||||||
| IPSec VPN | DES, 3DES, AES / MD5, SHA-1 / digital certificate and Chinese national-cipher certificate authentication / IKE main and aggressive mode / NAT traversal / DPD / zero-touch VPN onboarding with central management / IPSec VPN HA | |||||||||
| Reliability | Dual-device HA (active-active / active-standby) / IPSec VPN HA / hardware bypass and software bypass | |||||||||
| Management | Web / CLI / remote central management / cloud platform management / two-factor UKey authentication / port mirroring, link QoS statistics, packet capture in the web interface | |||||||||
| Configuration and upgrade | Configuration import/export, dual configuration backup / local and remote software upgrade | |||||||||
| SNMP | SNMP agent v1, v2, v3 | |||||||||
Firewall FAQ — ZTE Wantong ISG F-Series
How do I choose between the ten ISG F models?
Why are there two throughput figures per model?
Which models have 10G ports?
Can two units run as an HA pair, and what does bypass do?
What does "Xinchuang" mean for these firewalls?
Can I order under my own company name and use my own forwarder?
Can the firewall replace my internet router?
Can I add it to a running network without changing IP addresses?
How do branch offices connect to head office?
Can it handle guest or staff login on Wi-Fi?
What interfaces does the F24028X come with?
Can I order one unit first, and how does it reach my country?
How do I pay?
Related Products
Request a quote for this product
An engineer replies within 24 hours on working days with model check, price and lead time. No obligation, no newsletters.
Product: ZTE Wantong ISG F-Series · Xinchuang Firewalls